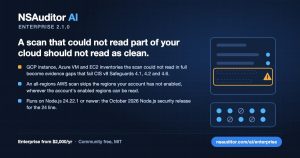
NSAuditor AI Enterprise 2.1.0: When the Scan Could Not Read Your GCP, Azure or EC2 Inventory, the Report Says So
A scan that could not read part of your cloud should not read as clean. When an assessor asks how...
A scan that could not read part of your cloud should not read as clean. When an assessor asks how...
What's new: GitLab has released fixes for a critical vulnerability (CVE-2026-110264) rated 10.0 on the CVSS scale, which allows unauthenticated...
Compliance evidence is usually a snapshot, and the posture underneath it keeps moving. A control that fails between audits stays...
An SLA report is a claim about time: how long a finding has been open, and how long it took...
Every scan diff has to decide what a missing finding means. If the second scan measured where the finding was...