Chainalysis Breach Exposes All Users’ Credentials, Forces Shutdown of Key Services
What's new: Chainalysis has reported a security breach that exposed all users' credentials, including names, usernames, password hashes, and live...
 Chainalysis Breach Exposes All Users’ Credentials, Forces Shutdown of Key Services
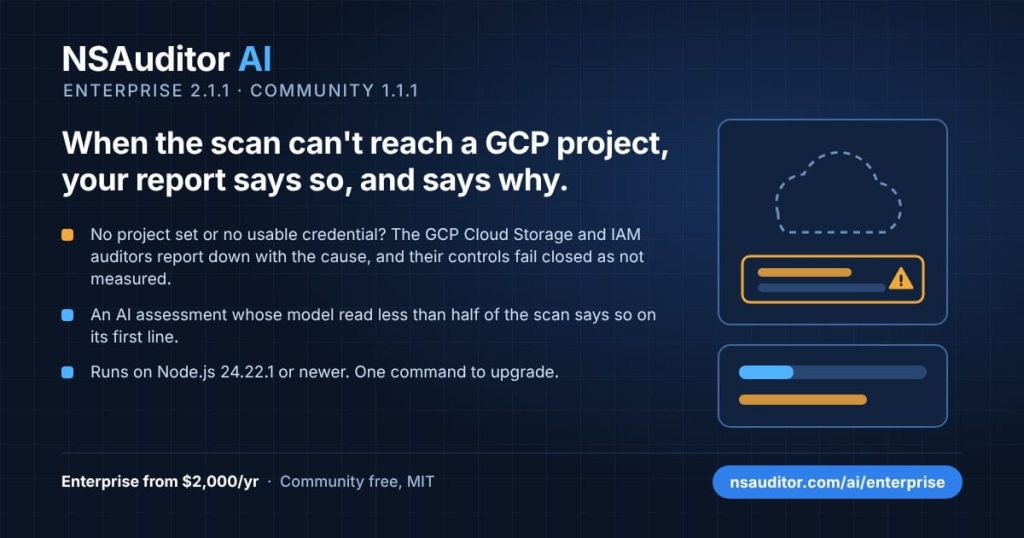
 NSAuditor AI Enterprise 2.1.1: When the Scan Cannot Reach Your GCP Project, the Compliance Report Says So, and Why
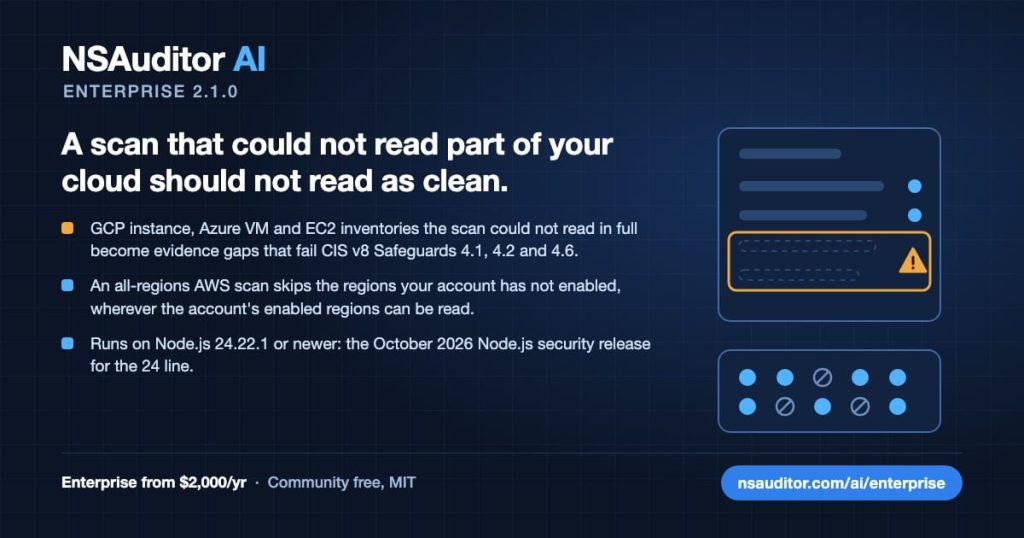
 NSAuditor AI Enterprise 2.1.0: When the Scan Could Not Read Your GCP, Azure or EC2 Inventory, the Report Says So
 Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
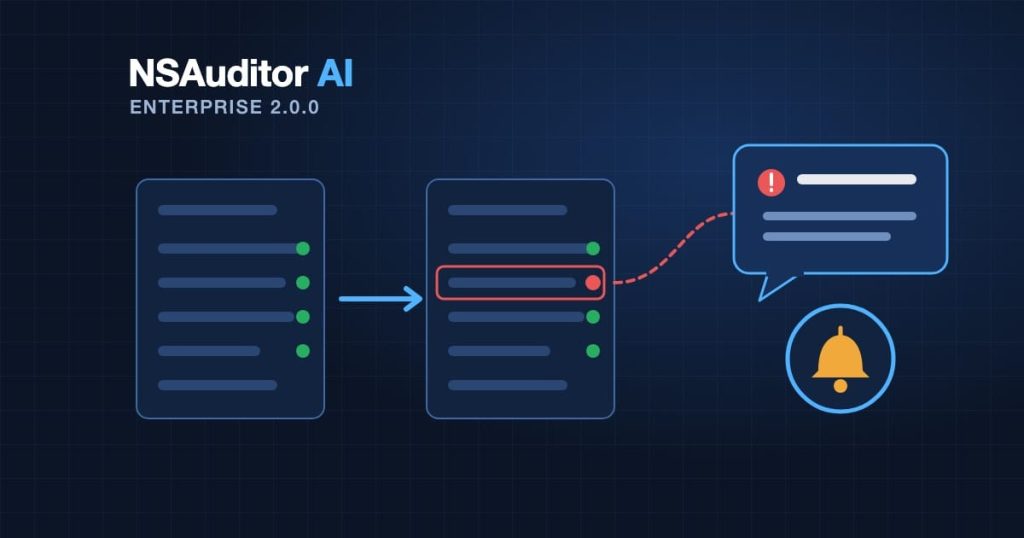
 NSAuditor AI Enterprise 2.0.0: Know What Changed Since the Last Compliance Scan, and Hear About It in Slack or Teams
What's new: Chainalysis has reported a security breach that exposed all users' credentials, including names, usernames, password hashes, and live...
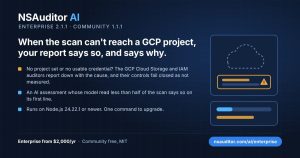
An assessor reading your evidence should be able to tell "measured and passed" from "not measured". NSAuditor AI Enterprise 2.1.1,...
A scan that could not read part of your cloud should not read as clean. When an assessor asks how...
What's new: GitLab has released fixes for a critical vulnerability (CVE-2026-110264) rated 10.0 on the CVSS scale, which allows unauthenticated...
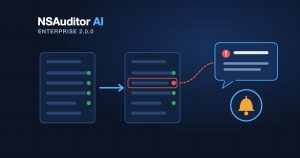
Compliance evidence is usually a snapshot, and the posture underneath it keeps moving. A control that fails between audits stays...